Professional services firms address growing cybersecurity needs
Key points:
- • Pittsburgh’s accounting, consulting, and law firms are helping clients treat cybersecurity as an enterprise-wide governance issue, not just an IT problem.
- • AI adoption is widening the gap between how secure companies feel and how prepared they are, which is driving demand for data governance and employee training.
- • Law firms are expanding cyber and privacy teams to handle breach response, regulatory investigations, and litigation for local healthcare, financial, and manufacturing clients.
 November 2026 — Pittsburgh’s professional services firms are fielding a steady rise in client questions about cybersecurity, data privacy, and the risks that come with artificial intelligence. The pressure is especially visible in the middle market. In RSM’s 2026 Middle Market Business Index, 18% of surveyed executives said their company suffered a data breach in the past year, and 24% reported at least one ransomware attack or demand. Additionally, only 35% of executives reported having a formal AI governance framework, even as 96% said they felt confident in their security measures, according to the report. That gap between confidence and preparation is where Pittsburgh’s accounting, consulting, and law firms are focusing their advice.
Join us at caa’s upcoming leadership summits! These premier events bring together hundreds of public and private sector leaders to discuss the challenges and opportunities for businesses and investors. Find the next summit in a city near you!
The region has a deep local base to draw on. Global firms with Pittsburgh offices are building on that foundation. PwC’s 2026 Global Digital Trust Insights survey drew on the views of 3,887 business and technology executives across 72 countries, and on the legal side, Chambers USA and Legal 500 rank Jones Day’s Cybersecurity, Privacy & Data Protection practice as a leading firm. Taken together, these efforts raise a practical question for local employers: how do they build the governance, data discipline, and workforce habits that hold up when the next threat arrives?
Professional services leaders from the Pittsburgh area, including Katie Mominee, office managing partner at PwC; Liz Krugliak, office leader of RSM Pittsburgh; Allison Sizemore, managing partner of Reed Smith; and Rebekah Kcehowski, partner-in-charge of Jones Day’s Pittsburgh office, shared their perspectives on how their firms are helping clients respond to growing cybersecurity needs.
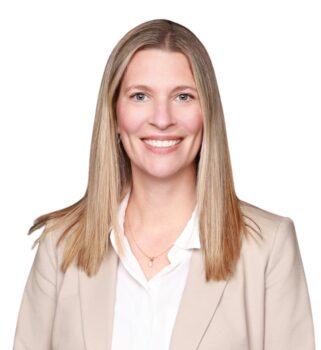 Katie Mominee, Office Managing Partner, PwC
Cyberattacks and emerging technology risks have become significant near-term concerns. As the landscape evolves, we are helping clients strengthen the governance structures they already have in place. Even governance developed one or two years ago may need to be modernized.
Organizations must reconsider their risk management practices, determine what risks they are willing to accept, and improve their cyber resilience. That may involve adopting new tools, working with new providers, and confirming their systems support the organization’s use of data and decision-making.
The quality and security of data remain central to building trust. Companies can develop excellent tools, but their data will remain at risk if they do not have effective governance and security or if employees fail to follow established protocols. The goal is to create an ongoing business capability that supports innovation rather than simply reacting to each new change or threat.
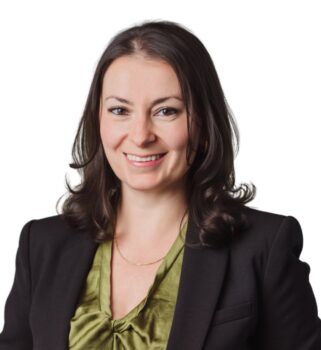 Liz Krugliak, Office Leader, RSM Pittsburgh
As cybersecurity threats and data privacy risks continue to evolve, organizations should prioritize building a comprehensive risk management strategy that combines strong governance, cybersecurity controls, data protection, and employee awareness across their entire footprint. Today’s threat landscape is no longer limited to external attacks. The rapid adoption of cloud technologies, AI, third-party platforms, and increasingly complex data ecosystems has expanded both the number of vulnerabilities and the potential business impact of a security incident.
The first priority should be data governance and visibility. Organizations need to understand what data they possess, where it resides, who has access to it, and how it is being used. As AI becomes more integrated into business processes, the ability to maintain accurate, secure, and well-governed data is increasingly critical. Strong data governance not only improves cybersecurity resilience but also supports privacy compliance and trusted AI adoption.
Regulatory compliance should be viewed as an ongoing process rather than a one-time exercise. Organizations operating across multiple jurisdictions face increasingly complex requirements related to privacy, data protection, reporting obligations, and industry-specific regulations in a changing world. Companies should continuously monitor regulatory developments, assess potential exposure, and align governance and compliance programs with their broader business strategy.
Finally, organizations should invest in workforce readiness. Technology alone cannot eliminate cyber risk. Employees remain one of the most important lines of defense, and organizations that foster a culture of security awareness, accountability, and ongoing education are often better equipped to manage emerging threats and reduce risk. As new technologies such as generative and agentic AI become more prevalent, employee understanding of secure and responsible usage will become increasingly important.
 Allison Sizemore, Managing Partner, Reed Smith
We are staying close to clients, concentrating on the industries we know best, and investing in talent and technology. Clients are managing uncertainty around changing trade policies, regulation, AI adoption, cybersecurity, costs, workforce, and risk management. Our goal is to assemble teams and be highly responsive to their needs as these issues evolve.
Reed Smith is growing in the areas and markets where our clients operate and anticipating the legal issues that they will need to solve to continue to be successful.
 Rebekah Kcehowski, Partner-in-Charge, Pittsburgh, Jones Day
Cybersecurity and data privacy are no longer niche concerns. These are board-level, enterprise-level risks. Jones Day is a leading firm in this space, and various industry recognitions rank our practices strongly. We can serve as a one-stop shop for clients dealing with breach preparedness, incident response, regulatory investigations, and privacy-related litigation.
In Pittsburgh, we see demand across the spectrum, including healthcare, financial institutions, and manufacturers with operational technology and trade-secret issues. The regulatory environment is evolving rapidly at federal and state levels. Clients need lawyers who understand the law, the technology, and the practical realities businesses face. We’ve invested in this work, including by adding cybersecurity and privacy partners. We can serve Pittsburgh companies navigating these issues and competing globally across jurisdictions and regions. This is a definite focus that our global reach allows us to serve from Pittsburgh.
Want more? Read the Invest: Pittsburgh report.